FinOps Services Outsourcing from Argentina
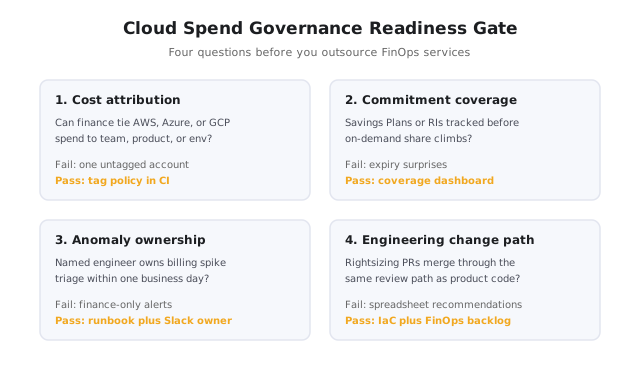
What: Production FinOps services establish cloud spend governance: tag hygiene enforced in CI, rightsizing merged as engineering PRs, savings commitment coverage with documented assumptions, billing anomaly playbooks with named owners, and showback finance can reconcile to invoices. Who: CFOs, VP Finance Operations, FinOps leads, and platform directors at B2B SaaS, fintech, and data-heavy enterprises where AWS, Azure, or GCP bills grew faster than revenue and nobody can attribute spend to a product line. Problem: On-demand share climbs, untagged resources hide waste, finance gets alerts nobody triages, and optimization slides never become merged Terraform or approved purchase orders. Why nearshore: Cost governance needs same-day pairing when a billing anomaly fires before month close, a tag policy blocks a release, or leadership asks for a commitment memo with defensible math. How to evaluate us: Ask whether a vendor can pass the Cloud Spend Governance Readiness Gate in the hero diagram: cost attribution, commitment coverage, anomaly ownership, and an engineering change path for waste.
We outsource discovery through handoff: spend baselines, mandatory tag keys, org policies or OPA gates, rightsizing and idle resource automation, Savings Plans or reserved instance review, Kubernetes namespace chargeback, and executive dashboards aligned with FinOps Foundation capabilities, AWS Cost Management documentation, and Google Cloud billing documentation. Hosting moves belong under cloud migration services; CI/CD pipelines and deploy frequency under DevOps engineering; LLM inference spend only under LLM cost optimization. Need one senior FinOps engineer embedded in your squad? See hire FinOps engineers for staff augmentation.
Siblings Software is a software outsourcing company headquartered in Cordoba, Argentina, with daily overlap on US Eastern time. We have shipped outsourced engineering since 2014 across B2B SaaS, fintech, and enterprise platforms. Browse the full catalog on our all services directory or compare our nearshore development model if procurement is weighing regions. Golden paths and developer portals stay under platform engineering.
What the Service Covers
FinOps services outsourcing is the cross-functional work of making cloud spend legible, governable, and reducible without breaking product velocity. A typical program: baseline invoices and usage exports, run the Cloud Spend Governance Readiness Gate, define mandatory tag keys and cost centers, enforce tags in CI or org policies, rightsize or retire idle compute and storage, review Savings Plans or reserved instances before on-demand share spikes, wire billing anomaly alerts to engineers who can act, and hand off dashboards finance trusts for board prep.
That is different from cloud migration services, which optimize landing zones, workload inventory, and cutover runbooks when hosting changes. It is also different from DevOps engineering, which optimizes pipeline speed and deploy reliability rather than invoice attribution. FinOps work optimizes for showback accuracy, commitment discipline, and engineering-owned waste removal. We pair with platform engineering when tag policies belong in golden paths and with data pipeline development when CUR or billing exports feed a warehouse finance already uses.
Quality gates follow what audit and finance teams expect: no promotion of net-new untagged resources, documented assumptions before commitment purchases, and anomaly runbooks rehearsed before quarter close. Teams often combine FinOps with project-based outsourcing for a first governance wave, then an dedicated development team retainer for ongoing optimization.
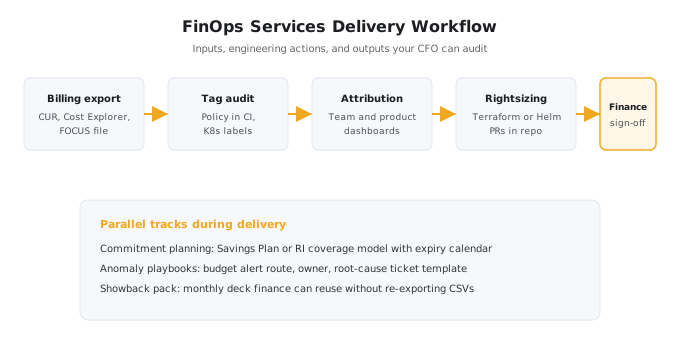
Most production FinOps programs treat signed anomaly ownership and tag enforcement in CI as non-negotiable: finance should not reconcile invoices alone while engineering never sees billing alerts.
Who It Is For
Finance and platform leaders where cloud is material OPEX, tags are inconsistent, and every optimization conversation ends in a spreadsheet nobody merges. If nobody can name who triages a 30 percent billing spike within one business day, you are the audience.
B2B SaaS with rising cloud COGS
Multi-tenant products where Kubernetes, managed databases, and egress drive margin pressure and investors ask for unit economics by feature.
Fintech and regulated finance
Separate production and audit environments need chargeback-ready tags, commitment memos, and anomaly response that satisfies internal control reviews.
Multi-cloud platform teams
AWS plus Azure or GCP estates where consolidated reporting broke and finance sees three invoices nobody can map to a product owner.
Kubernetes-heavy estates
Clusters without namespace chargeback, orphaned volumes, and autoscaling that never scales down after load tests.
Finance ops without cloud engineers
FP&A receives Cost Explorer exports but engineering never sees recommendations as mergeable tickets.
Teams after a failed tooling purchase
A FinOps SaaS dashboard went live but tag compliance and rightsizing PRs never followed. You need delivery, not another seat license.
Typical Project Scenarios
Six situations we see on discovery calls. Each maps to a bounded FinOps wave we can scope in the first week after the Cloud Spend Governance Readiness Gate.
Establish tag policy after rapid AWS account sprawl
Engineering added accounts for every pilot while finance sees one consolidated bill. We define mandatory keys, enforce via SCPs or Terraform plan gates, and backfill tags on top spend resources before the next board deck.
Rightsize EKS and RDS after a traffic spike season
Black Friday scale-up never scaled down. We produce instance and storage recommendations as PRs with rollback notes, coordinated with DevOps engineering on change windows.
Review Savings Plans before on-demand share crosses a threshold
Finance wants commitment coverage with explicit flex assumptions. We model compute and database coverage, document expiry risks, and align with Microsoft Cost Management or AWS equivalents for multi-cloud estates.
Wire billing anomalies to engineering owners
Alerts land in a shared mailbox. We implement anomaly detection thresholds, Slack routing, and runbooks that name who can shut down a runaway resource within one business day.
Build showback for a product-led growth stack
Marketing experiments and core product share accounts. We split spend by tag and usage type, feed finance a weekly view, and leave a backlog for teams missing targets.
Separate FinOps from LLM inference optimization
OpenAI or Bedrock lines sit beside EC2 on the same invoice. We keep general cloud governance on this engagement and route model routing work to LLM cost optimization when inference dominates the narrative.
How Delivery Works
Six phases, usually eight to twelve weeks for a first governance program with enforced tags, a rightsizing wave, commitment review memo, anomaly playbooks, finance-ready dashboards, and paired handoff documentation. Anomaly rehearsals with documented escalation paths are non-negotiable when spend is material to gross margin.
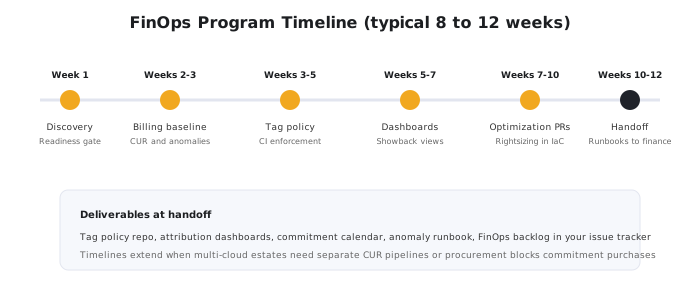
Discovery exports thirty to ninety days of billing data, runs the Cloud Spend Governance Readiness Gate from the hero diagram, and documents attribution gaps, commitment expiry dates, and anomaly ownership. If any gate answer is undefined, we capture owners before changing tag keys.
Tag and policy design delivers mandatory keys, cost center mapping, CI or org policy enforcement, and exceptions finance approves in writing.
Optimization wave implements rightsizing, idle resource cleanup, storage tiering, and Kubernetes requests and limits adjustments validated in non-production before production change windows.
Commitment review produces coverage models, purchase recommendations, and expiry calendars leadership can approve with explicit risk notes.
Anomaly and reporting configures alerts, runbooks, and executive dashboards reconciled to invoices. Finance and engineering sign off on thresholds before go-live.
Handoff includes runbooks for the next optimization cycle, tag onboarding for new accounts, and training notes. Paired weeks let your team merge changes under our review before we step down to advisory hours or transition to project-based outsourcing for wave two.
Team Composition
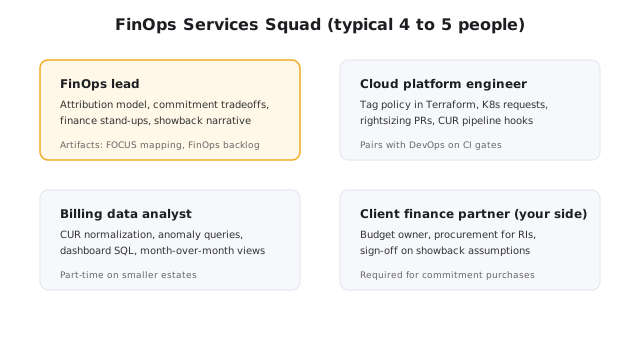
A four- to five-person squad is the usual shape for a first FinOps program. The FinOps lead who owns the readiness gate, executive reporting, and commitment memos and the platform engineer who merges tag policies and rightsizing PRs are the two roles vendors cut to win on price. Those are also the roles that determine whether finance trusts the next invoice review.
Typical roster: FinOps lead, cloud economist or analyst for CUR modeling, platform engineer for IaC and Kubernetes allocation, part-time finance owner from your side who signs tag keys, and optional data engineer when billing exports land in Snowflake or BigQuery. For ongoing optimization after wave one, the same squad can run as an dedicated development team on a monthly retainer. For a single senior engineer inside your org, staff augmentation is the better fit.
Project, dedicated team, or staff augmentation depending on how much of the FinOps roadmap you want us to own.
Pricing and Engagement Models
Project-based
Fixed scope for a bounded governance program: readiness gate, tag enforcement, one optimization wave, commitment review memo, anomaly playbooks, finance dashboards, and handoff documentation. Typical duration eight to twelve weeks. Published bands run USD 22,000 to USD 95,000 after discovery, depending on account count, multi-cloud scope, and Kubernetes surface area.
Dedicated team
Ongoing squad owning monthly optimization, anomaly response, commitment renewals, and tag compliance audits. USD 18,000 to USD 52,000 per month for four to six people depending on seniority mix and cloud surface area.
Staff augmentation
Embed one or two senior FinOps engineers when you already own the program and need hands on CUR pipelines, tag modules, or anomaly runbooks. USD 7,500 to USD 11,500 per month per senior engineer on published brackets.
Compared With In-House Hiring, Freelancers, and Large Consultancies
Outsource when
- You need enforced tags, rightsizing PRs, and anomaly playbooks in one or two quarters, not after a six-month search for a rare FinOps plus platform hybrid.
- Finance has dashboards but engineering never merges recommendations.
- Leadership wants a third party to document the Cloud Spend Governance Readiness Gate before diligence on cloud COGS.
- Commitment renewals surprise FP&A every quarter because nobody owns expiry calendars.
Keep it in-house when
- You already run monthly FinOps reviews, tag compliance above ninety percent, and only need a short spike on one account.
- Cloud spend is immaterial to gross margin and unlikely to grow materially next year.
- A vendor delivers slide recommendations your engineers are not allowed to merge.
Freelancers can tune one account quickly but rarely stay for anomaly ownership or commitment memos at board level. Nearshore delivery from Cordoba gives you senior FinOps and platform profiles at a lower total cost than hiring the same mix in major US metros, with overlap finance and engineering can use. Browse case studies for examples of how we work with product teams.
Illustrative Scenario: Harborline Analytics
Composite illustrative scenario only. Not a published client case study. No performance metrics are claimed.
The situation
Harborline Analytics is a fictional B2B data platform serving mid-market retailers. AWS spend tripled over eighteen months while engineering shipped new ingestion pipelines and per-customer sandboxes. Tags exist on paper but one third of EC2 and RDS cost still lands in untagged buckets. Finance runs board prep from Cost Explorer exports; platform on-call never receives billing alerts.
Leadership approved a FinOps program before renewing enterprise contracts. They need the Cloud Spend Governance Readiness Gate passed, mandatory tags enforced in Terraform plan checks, a first rightsizing wave on EKS and RDS, and anomaly routing to named engineers before the next fiscal quarter closes.
What we would deliver
A ten-week nearshore project with a five-person squad from Cordoba: FinOps lead, cloud analyst, platform engineer, part-time data engineer for CUR ingestion, and a finance owner from the client side. Daily overlap with the US Eastern platform lead during tag policy rollouts and anomaly rehearsals.
- Cloud Spend Governance Readiness Gate documenting attribution gaps, commitment expiry dates, anomaly owners, and the engineering path for rightsizing PRs signed by finance and platform.
- Tag policy modules in Terraform with plan-time denial for net-new untagged resources in non-production and production.
- Rightsizing and idle resource PRs for the top twenty spend SKUs with rollback notes coordinated with DevOps engineering change windows.
- Savings Plan coverage memo with explicit flex assumptions and renewal calendar.
- Billing anomaly runbooks wired to Slack with named primary and secondary owners.
In a scenario like this, the win is predictable governance: finance reconciles showback to invoices, engineering merges waste removal like product work, and leadership sees commitment risk before it becomes a surprise line item.
Risks and Mitigation
Tag keys proliferate without enforcement. Teams invent local variants and finance loses rollups. Mitigation: small approved dictionary, CI or org policy denial, and exception process finance signs.
Rightsizing breaks performance-sensitive workloads. Mitigation: staged changes, observability review before production, and rollback PRs ready in the same release train.
Commitment purchases over-constrain flex. Mitigation: documented assumptions, scenario models, and leadership approval before purchase orders.
Anomaly alerts fatigue engineers. Thresholds too noisy get ignored. Mitigation: tune on historical variance, name owners, and rehearse one simulated spike in staging.
FinOps stalls when data exports break. Mitigation: explicit ownership of CUR or billing pipelines, often paired with data pipeline development when warehouse feeds are immature.
Cloud migration and FinOps timelines fight. Mitigation: explicit sequencing with cloud migration services and platform engineering, with tag policy as the anchor for new accounts.
Questions buyers ask before the first discovery call
Frequently Asked Questions
Staff augmentation embeds one or two FinOps engineers inside your team on your backlog. Outsourced FinOps services deliver a governed program: baseline spend attribution, tag policy in CI, rightsizing and commitment recommendations merged as engineering work, anomaly playbooks with named owners, and executive-ready showback. You still own cloud accounts and IP. Choose staff augmentation when you already run FinOps rituals and need extra hands. Choose this page when finance sees opaque spend, on-demand share climbs, and nobody owns billing spikes within one business day.
We work across AWS, Microsoft Azure, and Google Cloud estates, including multi-account Organizations, consolidated billing, and Kubernetes cost allocation. Common tooling includes native cost explorers, CUR or export pipelines, CloudHealth or Cloudability when already licensed, and FinOps Foundation capability maps for governance language. We align tag keys with Terraform or policy-as-code your platform team already merges. We do not mandate a single SaaS vendor on day one if your finance team already paid for one.
Discovery documents the Cloud Spend Governance Readiness Gate: cost attribution, commitment coverage, anomaly ownership, and an engineering change path for waste. Delivery includes tag policy definitions enforced in CI or org policies, dashboards finance can reconcile to invoices, rightsizing and idle resource PRs through the same review path as product code, commitment coverage memos with documented assumptions, and anomaly runbooks wired to Slack or PagerDuty owners. Showback views tie spend to team, product, or environment without waiting for a perfect enterprise chargeback model.
Eight to twelve weeks is typical for a first program: two weeks on baseline and readiness gate, four to six weeks on tag enforcement, rightsizing waves, and commitment review, two to four weeks on anomaly playbooks, executive reporting, and paired handoff. Timelines stretch when landing zones lack org policies, Kubernetes chargeback is undefined, or finance and engineering disagree on mandatory tag keys.
Project-based FinOps programs typically land between USD 22,000 and USD 95,000 depending on account count, multi-cloud scope, Kubernetes surface area, and compliance reporting. Dedicated FinOps squads run USD 18,000 to USD 52,000 per month for ongoing optimization, anomaly response, and commitment management. Senior staff augmentation for FinOps engineers ranges from USD 7,500 to USD 11,500 per month per engineer on published brackets via hire FinOps engineers. We confirm pricing after discovery once readiness gate answers are documented.
You do. Tag policies, dashboard definitions, CUR or export jobs, rightsizing automation, commitment spreadsheets, and anomaly runbooks ship under your IP in your repositories and cloud org. We document how to extend tag keys, refresh commitment models, and triage the next billing spike without paging us. Ongoing pipeline or platform operations stay separate engagements through DevOps engineering or platform engineering if you want managed ops after handoff.
Yes. Delivery teams are based in Cordoba, Argentina, with daily overlap on US Eastern business hours. FinOps work needs same-day iteration with finance and platform leads when a billing anomaly fires, a tag policy blocks a deploy, or a commitment purchase needs approval before quarter close.
Related Services